
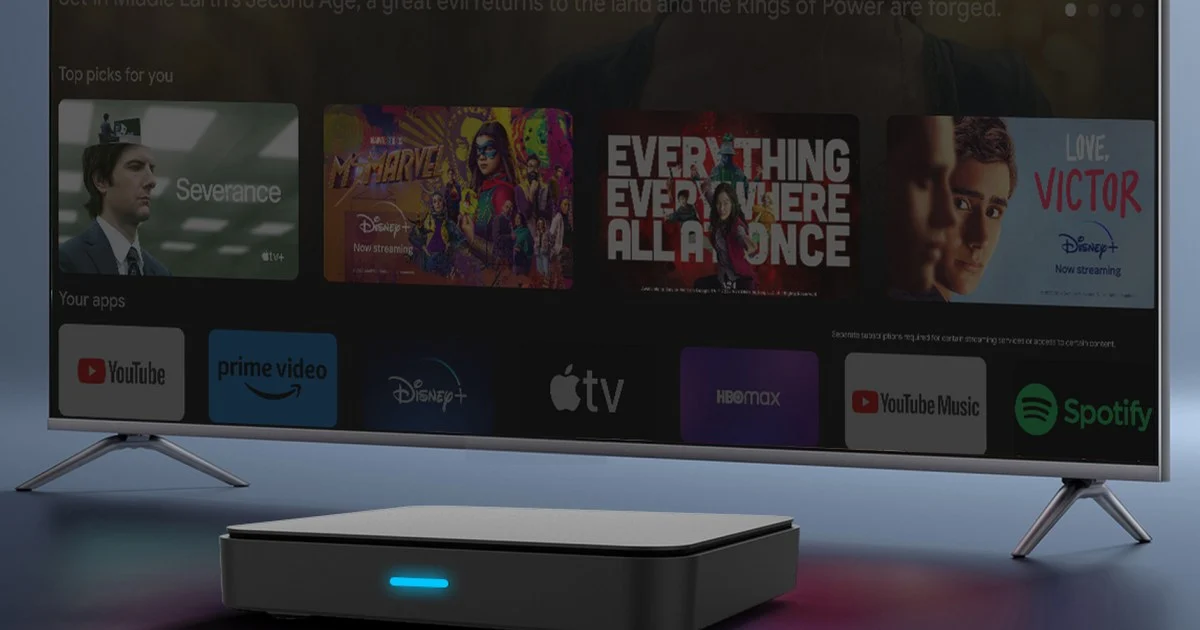
The digital world is constantly evolving, and with it, the threats to our personal data and devices. While we often focus on viruses and malware that infect our computers and phones, a more insidious threat can lurk within the very devices designed to connect us to entertainment and information. This threat comes in the form of botnets, networks of compromised devices controlled by cybercriminals. Recently, Google took down a massive botnet that had infected over 1.3 million Android TV set-top boxes, highlighting a disturbing trend: malware being pre-installed by manufacturers themselves. This situation serves as a stark reminder that even seemingly harmless devices can become tools for cybercrime, and understanding how these threats operate is the first step in protecting ourselves.
Understanding Botnets and Their Impact
A botnet is essentially a network of internet-connected devices, each infected with a malicious program called a “bot” or “zombie.” These bots are controlled remotely by a “botmaster,” who can command the entire network to perform various illicit activities without the device owners’ knowledge. The sheer scale of a botnet means that even a small number of compromised devices can be used for significant harm.
The impact of botnets can be far-reaching and devastating. Cybercriminals use them for a variety of malicious purposes, including:
- Distributed Denial of Service (DDoS) Attacks: Overwhelming a target server or website with traffic from thousands or millions of bots, causing it to crash or become inaccessible. This can disrupt businesses, government services, and online platforms.
- Spam Distribution: Sending out massive volumes of unsolicited emails, often containing phishing attempts or links to malicious websites.
- Data Theft: Stealing sensitive information such as login credentials, financial details, and personal data from compromised devices or through network sniffing.
- Ad Fraud: Generating fake clicks on online advertisements, defrauding advertisers and earning illicit revenue for the botmaster.
- Cryptocurrency Mining: Using the processing power of infected devices to mine cryptocurrencies, consuming significant electricity and slowing down the devices.
- Spreading Further Malware: Using the botnet as a platform to infect more devices and expand its reach.
The recent discovery by Google of the XCPE botnet, which compromised over 1.3 million Android TV boxes, illustrates a particularly alarming aspect of botnet operations. Unlike typical malware infections where users might unknowingly download a malicious app, this botnet’s origin was far more disturbing: the malware was embedded directly into the device’s firmware by the manufacturer, Videostrong Technology, a China-based company. This means that from the moment these devices were activated, they were already compromised and ready to be controlled by cybercriminals.
The XCPE Botnet: A Manufacturer’s Betrayal
The XCPE botnet, as detailed by Google’s Threat Intelligence Group, operated through a backdoor that was pre-installed in the firmware of Videostrong’s Android TV boxes. This backdoor was designed to be persistent, meaning it could download and install additional malware without the user’s consent or knowledge. Even if a user managed to remove the initial malware, the backdoor would simply reinstall it upon the device’s restart.
This covert operation allowed Videostrong to sell access to these compromised devices to criminal groups. These groups then utilized the botnet for a range of illicit activities, including advertising fraud, data theft, and rerouting internet traffic through unsuspecting users’ home connections. The scale of the operation was immense, with Google estimating that the takedown of the XCPE botnet infrastructure could also cut off access to over 10 million additional compromised devices.
The problem was not confined to just TV boxes. Google’s investigation revealed that similar malware was present on other devices manufactured by Videostrong, including telehealth devices, karaoke machines, and digital signage hardware. This broadens the scope of the threat, indicating that a wide range of consumer electronics could be vulnerable if manufacturers engage in such malicious practices.
How the Malware Operated
The core of the XCPE botnet’s success lay in its sophisticated and persistent nature. The backdoor, built directly into the device’s firmware, provided a direct line of communication to the botmaster. Once the device was powered on, this backdoor could execute commands remotely, allowing for the download and installation of various malicious payloads.
Here’s a breakdown of how the malware likely operated:
- Pre-installation: The malicious backdoor was embedded in the device’s firmware during the manufacturing process by Videostrong Technology. This bypassed any security checks that might occur during software installation by the end-user.
- Initial Activation: When a user first set up their Android TV box or other affected device, the pre-installed backdoor would activate.
- Command and Control (C2) Communication: The backdoor would establish a connection with a Command and Control server operated by the botmaster or their clients. This server would issue instructions to the infected device.
- Payload Download and Execution: Based on the commands received, the backdoor could download and install additional malware. This could include tools for data exfiltration, ad fraud modules, or components to participate in DDoS attacks.
- Persistence: A key feature of the XCPE botnet was its persistence. Even if users attempted to remove the malware through standard means, the backdoor in the firmware would ensure that the malicious software was reinstalled upon the next device reboot. This made it incredibly difficult for users to clean their devices.
- Exploitation: The botmaster would then sell access to these compromised devices, or use them directly, for various criminal activities. This could involve directing traffic through the devices, generating fake ad clicks, or using their IP addresses to mask other malicious activities.
The fact that the malware was integrated at the firmware level meant that it was deeply entrenched within the operating system. This is a far more serious threat than malware installed through applications, as it is much harder to detect and remove without specialized tools or replacing the entire firmware.
Google’s Response and Mitigation Efforts
Upon discovering the XCPE botnet, Google took swift action to disrupt the criminal operation. The company collaborated with security firms and Japan’s National Police Agency to dismantle the infrastructure used by the botnet. This involved taking down the Command and Control servers that were orchestrating the malicious activities.
Google’s response also included significant changes to its device certification processes. By banning Videostrong Technology from building or supplying software for certified Android devices, Google aims to prevent similar incidents from occurring with future Android-based products. This move signals a stronger stance against manufacturers who compromise user security for illicit gains.
Furthermore, Google has implemented enhanced device certification checks. These checks are designed to identify and flag devices that may contain pre-installed malware or backdoors. This proactive measure helps to ensure that only devices meeting Google’s security standards are allowed to be certified and distributed within the Android ecosystem.
What Users Can Do to Protect Themselves
The XCPE botnet incident serves as a wake-up call for consumers regarding the security of their smart devices. While manufacturers like Google are working to secure the ecosystem, users also play a critical role in protecting themselves.
Here are several steps users can take to mitigate the risks associated with compromised smart devices:
- Purchase from Reputable Manufacturers: Always buy electronic devices, especially smart home devices and media streamers, from well-known and trusted brands. These companies generally have more robust security practices and a greater incentive to maintain customer trust. Avoid unknown brands or suspiciously cheap devices, as they may cut corners on security.
- Keep Google Play Protect Enabled: For Android devices, ensure that Google Play Protect is enabled. This feature scans apps for malicious behavior and helps protect your device from malware. It’s a crucial layer of defense, even if the primary threat comes from pre-installed firmware.
- Update Device Software Regularly: Manufacturers often release software updates that include security patches. It’s essential to install these updates promptly to fix any vulnerabilities that may have been discovered. For smart TVs and streaming devices, check for system updates in the device’s settings menu.
- Be Wary of Unknown Devices: If you have a device manufactured by Videostrong Technology, Google strongly recommends disconnecting it from the internet immediately. Given the deep-seated nature of the malware, it is best to replace such devices with those from trusted brands.
- Secure Your Home Network: Your home Wi-Fi network is the gateway to all your connected devices. Use a strong, unique password for your router and enable WPA2 or WPA3 encryption. Consider segmenting your network if possible, creating a separate network for IoT devices that might be less secure.
- Monitor Network Traffic (Advanced): For more technically inclined users, monitoring network traffic can help identify suspicious activity. If a device is communicating with unknown servers or sending out unusual amounts of data, it could be a sign of compromise.
- Disable Unused Features: If your smart TV or streaming device has features you don’t use, consider disabling them. This reduces the potential attack surface for malware. For example, if you don’t use voice commands, you might be able to disable the microphone.
- Read Reviews and Research: Before purchasing any smart device, take the time to research the brand and model. Look for reviews that mention security features or any reported vulnerabilities. Online forums and tech news sites can be valuable resources.
The Broader Implications for the Internet of Things (IoT)
The XCPE botnet incident is not an isolated event but rather a symptom of a larger, growing problem within the Internet of Things (IoT) ecosystem. As more devices become connected to the internet, from smart refrigerators and thermostats to security cameras and even children’s toys, the potential attack surface for cybercriminals expands exponentially.
Many IoT devices are designed with cost and convenience as primary drivers, often at the expense of robust security. Manufacturers may not have the expertise, resources, or motivation to implement strong security measures, leaving devices vulnerable to exploitation. This can lead to devices being recruited into botnets, used for surveillance, or becoming entry points into a user’s home network.
The fact that a manufacturer would intentionally embed malware into its devices is a grave concern. It erodes trust in the entire IoT market and highlights the need for greater accountability and regulation. Consumers are increasingly relying on these devices for daily life, and the idea that they could be unknowingly participating in criminal activities is deeply unsettling.
Several factors contribute to the vulnerability of IoT devices:
- Lack of Regular Updates: Unlike computers and smartphones, many IoT devices do not receive regular security updates, if they receive them at all. This leaves known vulnerabilities unpatched and exploitable.
- Weak Default Passwords: Many devices ship with default passwords that are easily guessable or widely known, making them simple targets for attackers.
- Insecure Network Protocols: Some devices use outdated or insecure network protocols that can be easily intercepted or manipulated.
- Limited Processing Power: Some low-cost IoT devices have limited processing power, which restricts their ability to run complex security software or encryption.
- Supply Chain Vulnerabilities: As seen with the XCPE botnet, threats can be introduced at various points in the supply chain, from component manufacturing to software development.
Addressing these challenges requires a multi-faceted approach involving manufacturers, regulators, and consumers. Manufacturers need to prioritize security from the design phase, implement secure coding practices, and provide ongoing support through updates. Regulators may need to establish minimum security standards for IoT devices. Consumers, in turn, must become more informed and vigilant about the devices they bring into their homes.
The Future of Smart Device Security
The incident involving the XCPE botnet underscores the critical need for enhanced security measures across the entire spectrum of connected devices. Google’s proactive stance in shutting down the botnet and strengthening its certification processes is a positive step. However, the underlying issues of supply chain security and manufacturer accountability remain significant challenges.
As technology advances, so too will the methods employed by cybercriminals. The trend of embedding malware at the firmware level is particularly concerning because it is so difficult to detect and remove. This highlights the importance of:
- Firmware Integrity Checks: Developing better methods for verifying the integrity of device firmware, both during manufacturing and throughout the device’s lifecycle.
- Supply Chain Security: Implementing stricter controls and audits throughout the supply chain to prevent malicious components or software from being introduced.
- Transparency and Accountability: Encouraging greater transparency from manufacturers regarding their security practices and holding them accountable for breaches caused by negligence or malicious intent.
- Consumer Education: Continuously educating consumers about the risks associated with connected devices and empowering them with the knowledge to make informed purchasing decisions and adopt secure practices.
The digital landscape is a shared responsibility. While technology companies like Google play a vital role in defending against cyber threats, the security of our connected lives ultimately depends on a collective effort. By understanding the threats, adopting best practices, and demanding higher security standards, we can work towards a safer and more trustworthy digital future for all our devices.
Conclusion
The takedown of the XCPE botnet, which compromised over 1.3 million Android TV boxes due to pre-installed malware by the manufacturer Videostrong Technology, serves as a critical warning. It demonstrates that threats can originate not just from malicious apps downloaded by users, but from the very devices themselves, compromised at the manufacturing stage. This incident highlights the pervasive nature of cyber threats in the expanding Internet of Things (IoT) ecosystem and the profound impact they can have on unsuspecting consumers.
Google’s swift response, including disrupting the botnet’s infrastructure and strengthening its device certification processes, is commendable. However, the incident also underscores the urgent need for greater vigilance from consumers and a commitment to security from manufacturers. By prioritizing reputable brands, keeping software updated, and securing home networks, individuals can significantly reduce their risk. The ongoing evolution of cyber threats demands continuous adaptation and a shared commitment to building a more secure digital environment for everyone.
Conversation
0 Comments